Network & Endpoint Security FOR Canada
Network and Endpoint Security That Shows Its Work
Telnet Networks designs, supplies and supports the whole chain: complete traffic access, detection you can explain, validation that your defences hold, and the evidence to prove it. Delivered by a Canadian team, on-premise or fully air-gapped.
Canadian team, CAD pricing
On-prem or air-gapped
300+ organizations served
Or call 1 800 561 4019 · sales@telnetnetworks.ca
We reply within one business day, usually within a couple of hours.
The Telnet Security Stack
01
Complete, lossless traffic from every segment that matters.
02
Findings with the evidence and logic behind them, not alert queues.
03
Test that your controls hold before an attacker does.
04
Keep the records auditors, regulators and your board ask for.
Your Security Tools Are Only as Good as What They Can See
Attackers spend months inside networks their owners believed were protected, and most breaches are found by someone else. The gap is rarely a missing product. It is missing visibility, findings nobody can explain, and no record to learn from.
150 days
The average time an attacker is in the network before discovery.
84%
Of these breaches are discovered by an external entity.
Blind spots hide the first move
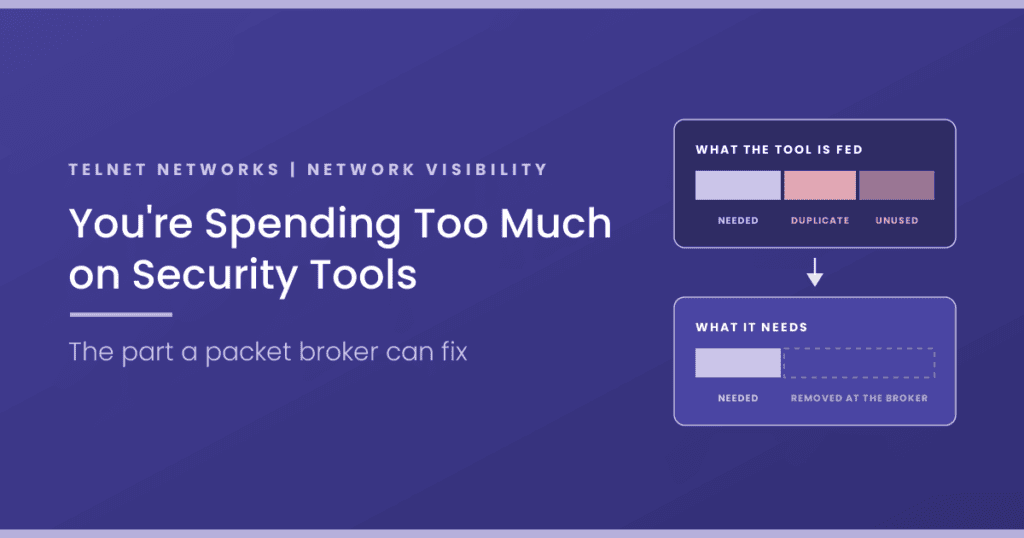
SPAN ports drop packets, and encrypted or east-west traffic never reaches your tools. Complete traffic access comes first.
Black-box alerts cost analyst hours
A queue of scores nobody can explain gets ignored. Findings that show their logic and their evidence get acted on.
No record means no answers
When an auditor, regulator or board asks what happened, you need timelines and evidence, not recollection.
Four Layers, One Accountable Partner
Most security programs are bought as separate products from separate vendors. We scope them as one chain, so each layer feeds the next and the whole thing stays in your custody.
Layer 1
Access
Complete, lossless traffic from the segments that matter, IT and OT: TAPs, packet brokers, inline bypass and hardware data diodes.
Partners: Garland, Cubro, Profitap, Keysight
Layer 2
Detect
Network detection and response that explains itself: timelines, protocol logs and the logic behind every finding. On-prem or fully air-gapped.
Partners: Stamus Networks, CySight
Layer 3
Validate
Breach and attack simulation and security testing, so you know your controls hold before an attacker finds out they do not.
Partner: Keysight
Layer 4
Prove
Evidence trails from traffic to finding to test result, held in your own custody and ready for auditors, regulators and Bill C-8 reporting.
Built from: layers 1 to 3
Detect: Stamus Clear Turns Traffic Into Evidence
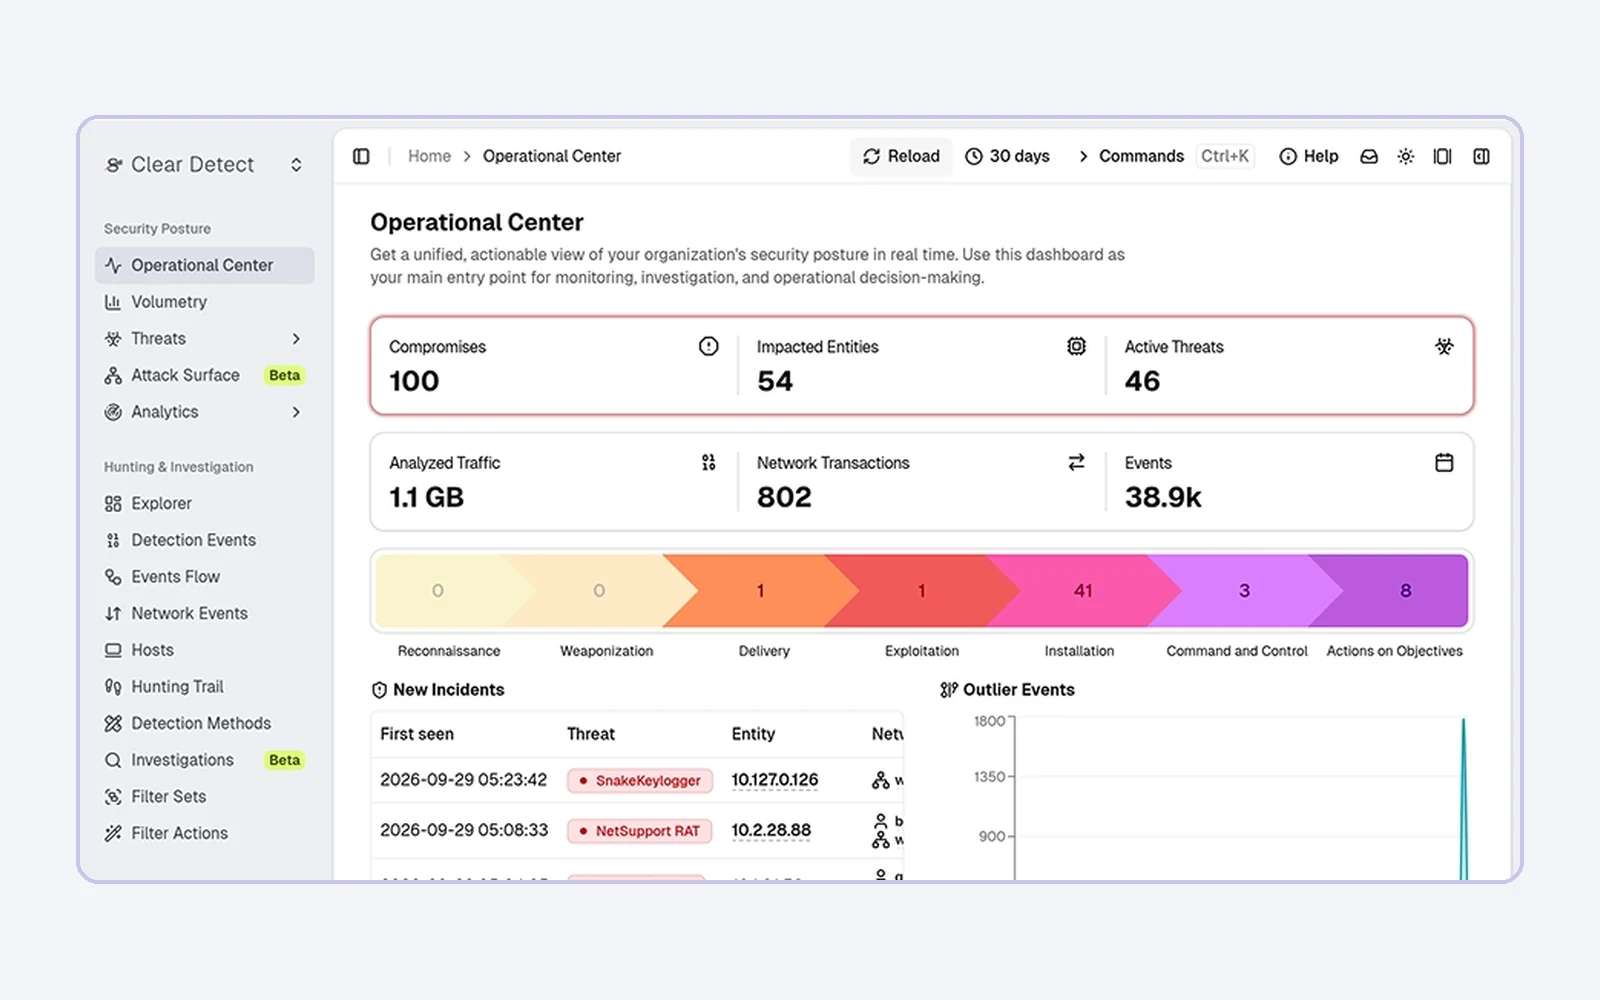
Telnet Networks is a Stamus Networks Solution Delivery Partner, focused on Canada. Stamus Clear watches the one layer every attacker has to cross, the network, and hands your team a short list of response-ready cases.
Layer 2 · Detect · Lead partner
Evidence-Backed Network Security, On Your Terms
Stamus Clear runs on-premise, in a private cloud or fully air-gapped, with no dependency on a vendor cloud. It is built on Suricata by the people behind it, so you can read the logic that fired and defend every finding.
• Declarations of Compromise and Policy Violation, not alert queues
• Timelines, protocol logs and conditional PCAP behind every case
• Passive and agentless: SPAN or TAP only, nothing installed on the assets you protect
• Covers enterprise IT and OT, ICS and SCADA networks
10 years
in NATO’s largest cyber exercises
97%
net customer retention
4.7 / 5
Gartner Peer Insights rating
Also available: CySight, agentless network detection and forensics built on flow data from your existing network equipment. Learn more about CySight →
Validate: Security Testing with Keysight
Keysight's security testing tools show whether your security controls actually work. Breach and attack simulation and realistic threat traffic test your defences across a full range of attack vectors before a real attacker does.
Breach and Attack Simulation
Keysight Network Security Suite
Keysight's network test and security solutions support dynamic security intelligence. They validate your security posture using real applications and threats, so you find the gaps before anyone else does.
Threat Simulator
Breach and attack simulation to test your security controls
BreakingPoint
Application and attack traffic, including DDoS simulation
CyPerf
Security and performance testing for cloud and hybrid environments
Application and Threat Intelligence (ATI)
Current applications and attacks for realistic test traffic
Cyber Range and IoT Security Assessment
Hands-on security exercises and assessment of connected IoT devices
7
tools in the Keysight Network Security Suite
Full
range of threat vectors covered by Keysight testing
Real
applications and threats used to test your security posture
Access Hardware for Complete Network Visibility
Detection and testing only work on traffic you can actually see. Our TAP and packet broker partners supply the access layer underneath, and we help you choose the right fit.
TAPs, Aggregators and Bypass
Garland Technology
Purpose-built network TAPs, packet brokers and bypass switches for permanent, passive access to copper and fibre links.
Best for: Critical links that need always-on access
Explore Garland Solutions
Packet Brokers, TAPs and DPI
Cubro
Network packet brokers and TAPs for high-density aggregation and filtering, including carrier and 5G environments.
Best for: High-density aggregation and traffic filtering
Explore Cubro Solutions
TAPs and packet Capture
Profitap
Network TAPs plus capture and analysis tools for troubleshooting and security monitoring.
Best for: Capture and analysis alongside TAP access
Explore Profitap SolutionsNetwork and Endpoint, Working Together
Endpoint tools see what happens on a device that can run an agent. Network evidence sees what happens between devices, including the systems that cannot run an agent. The strongest programs use both.
Works With Your EDR
Network findings flow into your SIEM, SOAR, EDR and firewalls, so they land where your team already works.
Covers Devices That Can't Run an Agent
OT controllers, IoT, printers and legacy systems still show up on the network, even where no endpoint tool can be installed.
Fills Your EDR Blind Spots
Already running EDR? We will show where network evidence closes the gaps, from lateral movement to unmanaged devices.
Where This Stack Is Deployed
From carrier cores to substations and trading floors, the same four layers adapt to how each sector runs and to the rules it answers to.
Telecommunications
Network evidence that supports incident reporting and supply-chain scrutiny.
Energy and Utilities
Passive monitoring for substations and control networks, where an agent will never be installed.
Federal Government and Defence
Segmented, air-gapped and classified environments where detection must run on-prem and traffic access has to be passive and auditable.
Financial Services
Explainable detections that stand up to auditors and regulators.
Municipal Government
City and regional networks that run public services, with lean IT teams and growing expectations to detect threats and prove controls work.
Transit
Rail, bus and transportation networks where signalling, operations and passenger systems all need visibility and early threat detection.
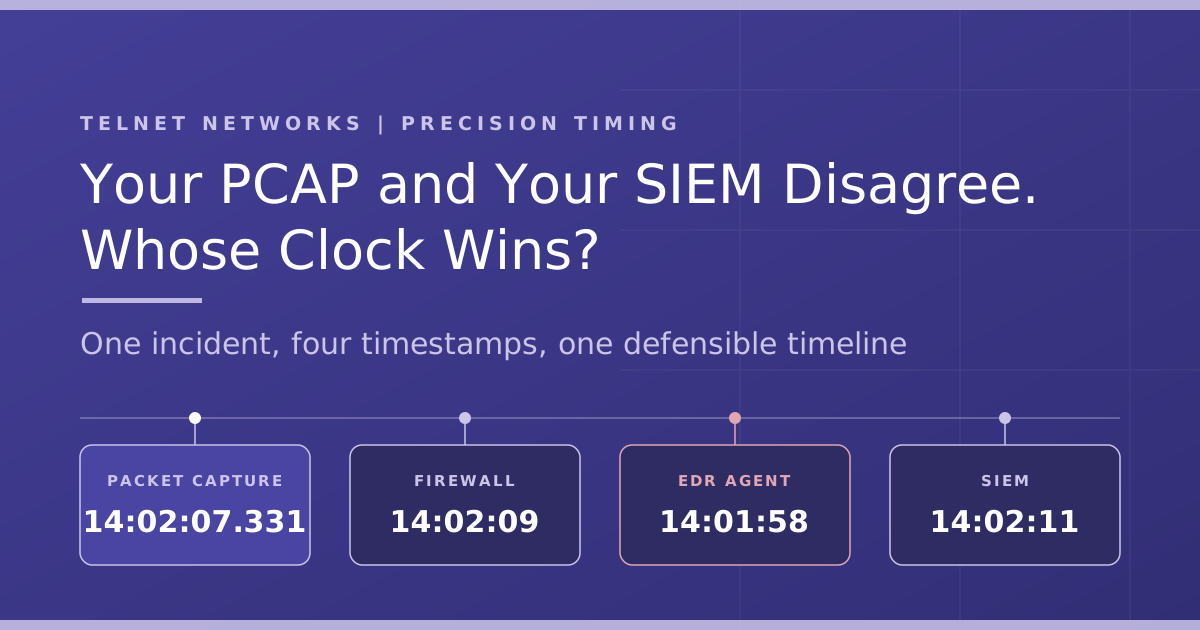
Timing Matters
Accurate Time Makes Security Evidence Hold Up
Detections, logs and packet captures only line up if every device agrees on the time. Precise, synchronized timestamps keep incident timelines reliable across systems and defensible for auditors.
Which Layer Do I Need First?
Start from the problem you have today. Most projects begin with one layer and add the next as the program matures.
Your situation
Start with
Partners
Why
Security tools are blind to parts of the network
Access
Garland, Cubro, Profitap TAPs and packet brokers
Complete, lossless copies of traffic, with no SPAN drops
Alerts nobody can explain or defend
Detect
Stamus Clear
Findings with timelines, protocol logs and readable logic
An OT or classified network must be watched with no way back in
Access + Detect
Garland data diodes with Stamus Clear
Physical one-way separation feeding passive detection
A firewall or IPS in the path must not become an outage
Access
Inline bypass from Garland or Cubro
Hardware bypass keeps the link up if the tool fails
Not sure the controls you bought actually work
Validate
Keysight breach and attack simulation
Test with real applications and a full range of threat vectors
Security tools need decrypted, filtered traffic
Access
Keysight security-enabled packet brokers
SSL decryption and per-tool filtering give each tool only what it needs
Need to stress-test network and security tools before go-live
Validate
Keysight BreakingPoint, CyPerf and Threat Simulator
Realistic application and attack traffic exposes gaps before an attacker does
Already running EDR, a SIEM or SOAR
Detect
Stamus Clear plus your existing stack
Network evidence flows into the tools you already use to enhance the security picture
Encrypted traffic, with no appetite to decrypt it
Detect
CySight
Flow-based behavioural analysis of encrypted traffic without packet decoding
Not sure? Send us a short description of your environment and we will recommend where to start.
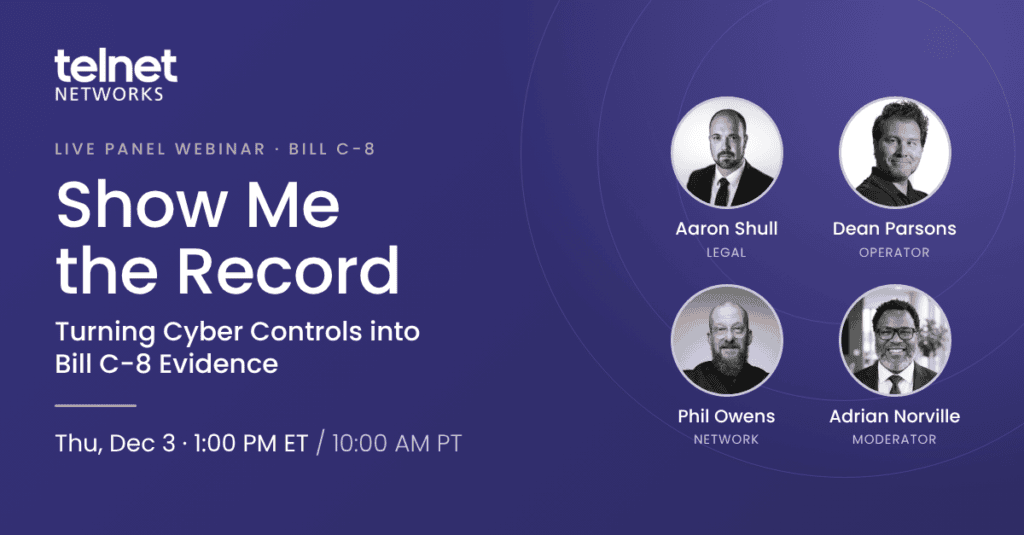
Describe your environmentBill C-8
Preparing for Bill C-8?
Book a 45-minute C-8 Readiness Briefing: what the Act requires, where evidence gaps usually sit, and how network evidence helps you prepare.
Request a quote
Tell Us What You Need to See, Detect and Prove
Describe your environment and what keeps you up at night. We reply within one business day, usually within a couple of hours, with a recommendation and next steps.
Request a quotePrefer to talk it through first? Book a 20-minute consult or call 1 800 561 4019.
Common Questions About Network and Endpoint Security
What is the difference between network detection and endpoint detection?
Endpoint tools watch what happens on the device they are installed on. Network detection watches the traffic between devices, including systems that cannot run an agent, such as OT, IoT and legacy equipment. They answer different questions, and the strongest programs use both.
Can network detection run on-premise or fully air-gapped?
Yes. Stamus Clear deploys on-premise, in a private cloud or fully air-gapped, with no dependency on a vendor cloud. For the most sensitive networks, Garland hardware data diodes give the monitoring feed a physical one-way path.
Do I need new TAPs and packet brokers first?
Not always. If you already run taps and brokers, Stamus Clear adds to your existing visibility fabric. If you rely on SPAN ports today, you can leverage that or we scope traffic access so the detection layer sees complete, lossless traffic.
Where does Keysight fit alongside Stamus?
Stamus Clear detects threats and explains each finding with its evidence. Keysight tests whether your security controls hold with breach and attack simulation. Most programs use both, and we scope them together.
Can I try it before I buy?
For qualified projects, yes. We provide evaluation units under Telnet’s standard hardware evaluation agreement, and a Stamus Clear proof of concept can run on your existing visibility infrastructure. Tell us what you want to prove and we will propose a plan.
Do you quote in Canadian dollars and support us locally?
Yes. Telnet Networks quotes and invoices in CAD and handles the import, so you deal with one Canadian vendor. Pre-sales and post-sales support come from our team in Ontario, in your time zone.