Skip to content
Stamus Networks

Stamus Networks: Evidence-Backed Network Security, On Your Terms

Stamus Clear turns network traffic into clear, evidence-backed answers about what is happening on your network. On-premise, private cloud or fully air-gapped, with no dependency on a vendor cloud. Telnet Networks is a Stamus Networks Solution Delivery Partner, focused on Canada and also serving the US and the Caribbean.

Built on Suricata. Built for Defenders.

Stamus Clear watches the one layer every attacker has to cross: the network. Probes inspect all traffic passively, and the central server correlates findings into a short list of response-ready cases.

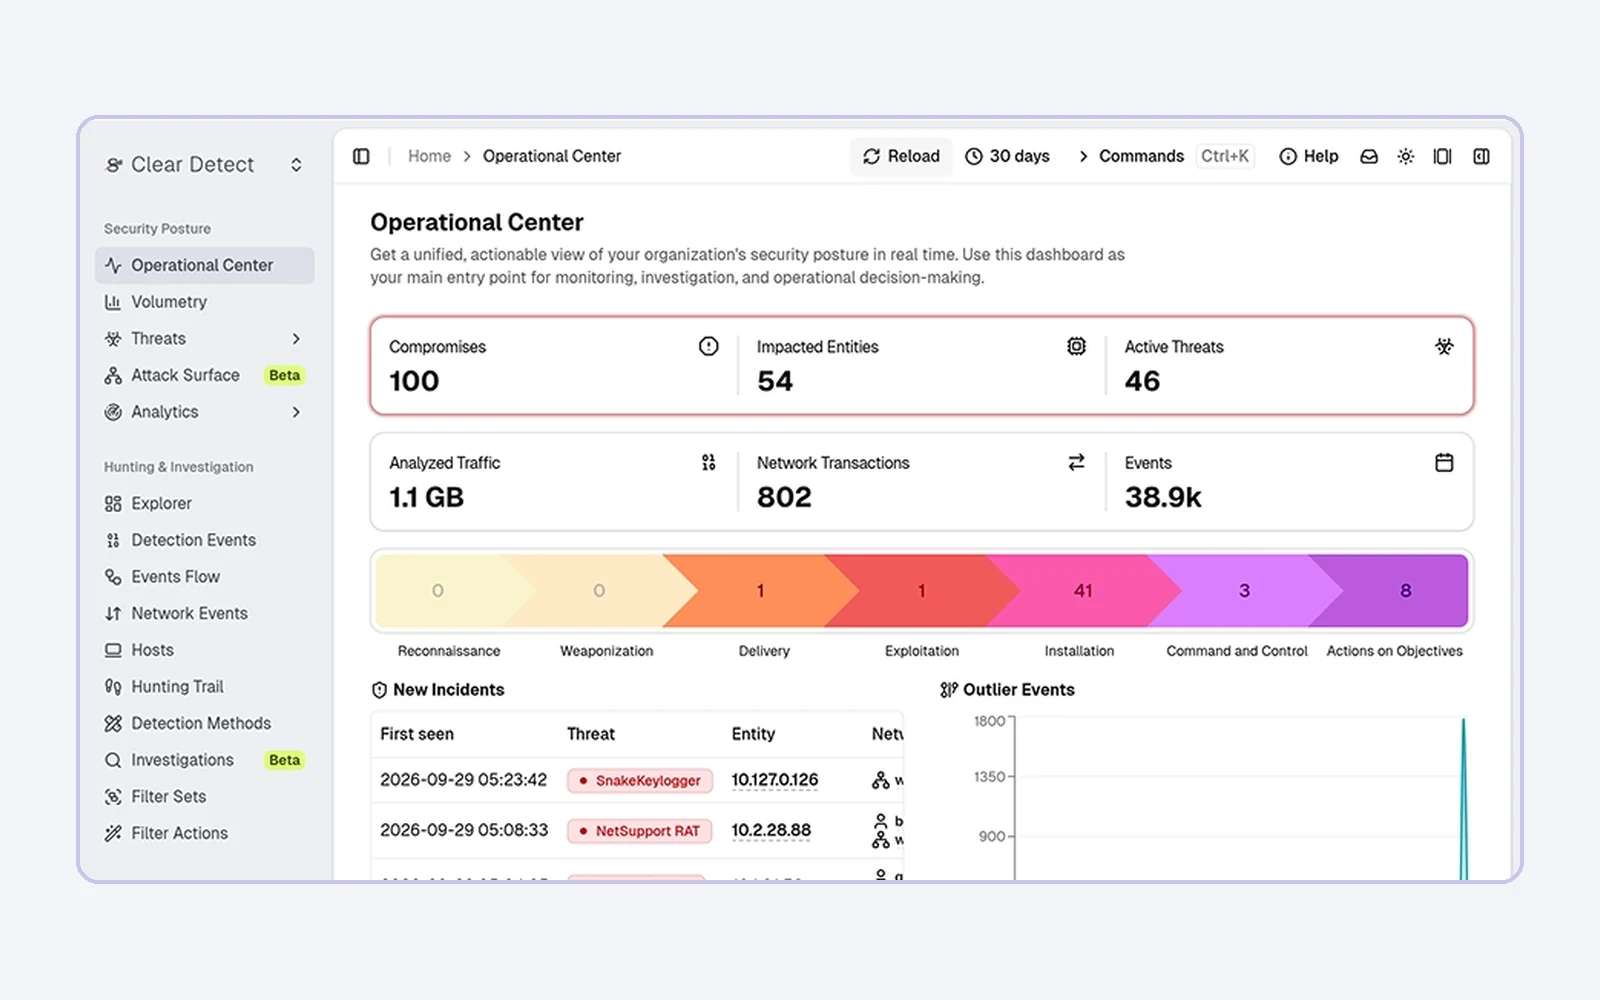
Stamus Clear Detect Operational Center dashboard showing compromises, impacted entities, active threats, a kill chain breakdown and new incidents

Enterprise IT networks

Data centre, campus, branch and hybrid cloud.

Probes analyze IT traffic in real time and capture protocol transactions; the central server adds machine-learning and algorithmic detection, automated triage, threat hunting and integrations with your SIEM, SOAR, EDR and firewalls.

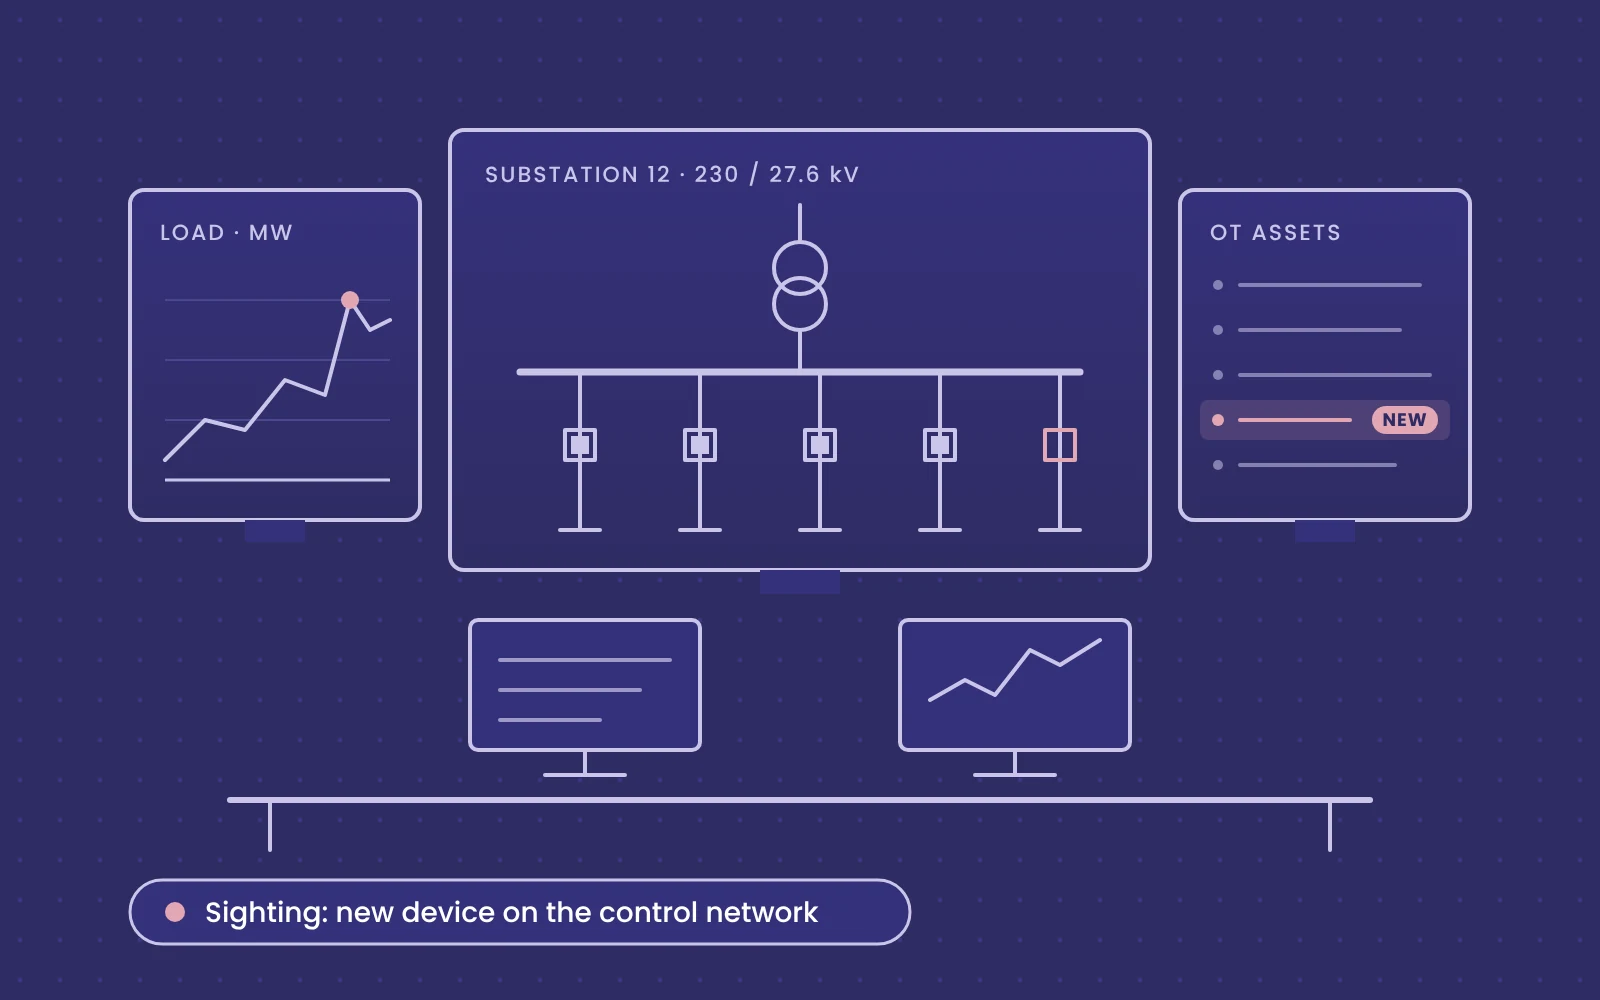
Illustration of an OT control room with a substation single-line diagram, load trend and asset list, flagging a Stamus Clear sighting of a new device on the control network

OT, ICS and SCADA

Substations, plants, pipelines and signalling networks.

Passive monitoring for industrial networks, with no agents and no scanning. SIGHTINGS flag anything seen for the first time on a network that should never change.

IEC-104 Modbus DNP3 ENIP/CIP S7 BACnet OPC MQTT

Stamus + Telnet Networks: From the Fibre to the Finding

Network-based detection is only as good as the traffic it is fed. For more than two decades, Telnet has designed and supplied the visibility fabric (taps, packet brokers and aggregation) that Canadian organizations of every size and sector run. We scope the traffic access, Stamus Clear turns it into evidence, and the whole chain stays in your custody. Already running taps and brokers? Stamus Clear adds to your existing fabric.

Schedule Consultation

Sovereign by design

On-prem, private cloud or air-gapped. Your data never leaves your custody.

Evidence with every finding

Timelines, protocol logs and conditional PCAP behind each case.

Logic you can read

Inspect the detection logic that fired. No black-box scores.

Passive, no agents

SPAN or tap only. Nothing installed on the assets you protect.

How It Works

One pipeline, one accountable partner, from traffic access to a declared finding.

Your network

IT and OT segments

→

TELNET

Taps + brokers

Complete, lossless access

→

STAMUS CLEAR

Probes + server

Detect, triage, declare

→

Your SOC tools

SIEM, SOAR, data lake

Everything stays inside your custody boundary

Step 1 · Access

Telnet taps and packet brokers

Deliver complete, lossless traffic from the segments that matter.

Step 2 · Detect

Stamus Clear probes

Decode and inspect it, with 100,000+ detection methods at up to 100 Gbps per probe.

Step 3 · Declare

Declarations, with evidence

High-confidence Declarations of Compromise and Policy Violation, sent to your SIEM, SOAR or data lake.

Industry Tailored Solutions

Telecommunications

Telecom obligations under Bill C-8 are already in force. Network evidence that supports incident reporting and supply-chain scrutiny.

Energy and Utilities

Passive monitoring for substations and control networks, where an agent will never be installed and new behaviour is the signal.

Government and Defence

Air-gapped deployment with no vendor cloud, backed by ten years supporting NATO cyber defence exercises.

Financial Services

Explainable detections that stand up to auditors and regulators, trusted by European central banks.

Why Stamus

Open. Transparent. Proven.

Open by Design

Built on Suricata by the people behind it, with a community edition and open integrations.

Transparent Detections

Every finding shows its logic and evidence, so you can defend it to a board, auditor or regulator.

Proven Where It Matters

Trusted by central banks, government CERTs and critical infrastructure operators.

10 years

in NATO's largest cyber exercises

97%

net customer retention

Since 2014

building on Suricata

Preparing for Bill C-8?

Book a 45-minute C-8 Readiness Briefing: what the Act requires, where evidence gaps usually sit, and how network evidence helps you prepare. Or ask about a proof of concept on your existing visibility infrastructure.

Book a Briefing

Related Posts