OT network change detection sounds like a compliance checkbox. In practice, it is one of the most precise detection methods a plant, substation, or pumping station has, because those networks are engineered not to change. A remote terminal unit polls the same two masters for years. An HMI talks to one historian. When something new shows up, it is worth an immediate look.
It is also where most security stacks go quiet. Endpoint agents are rarely an option on vendor-managed HMIs or PLCs, and active scanning risks operational disruption. In much of OT, the network is the only place left to watch.
That is the core thesis behind Nothing Should Ever Be New Here, a technical brief from our partner Stamus on behavioural detection for OT, ICS, and SCADA networks.
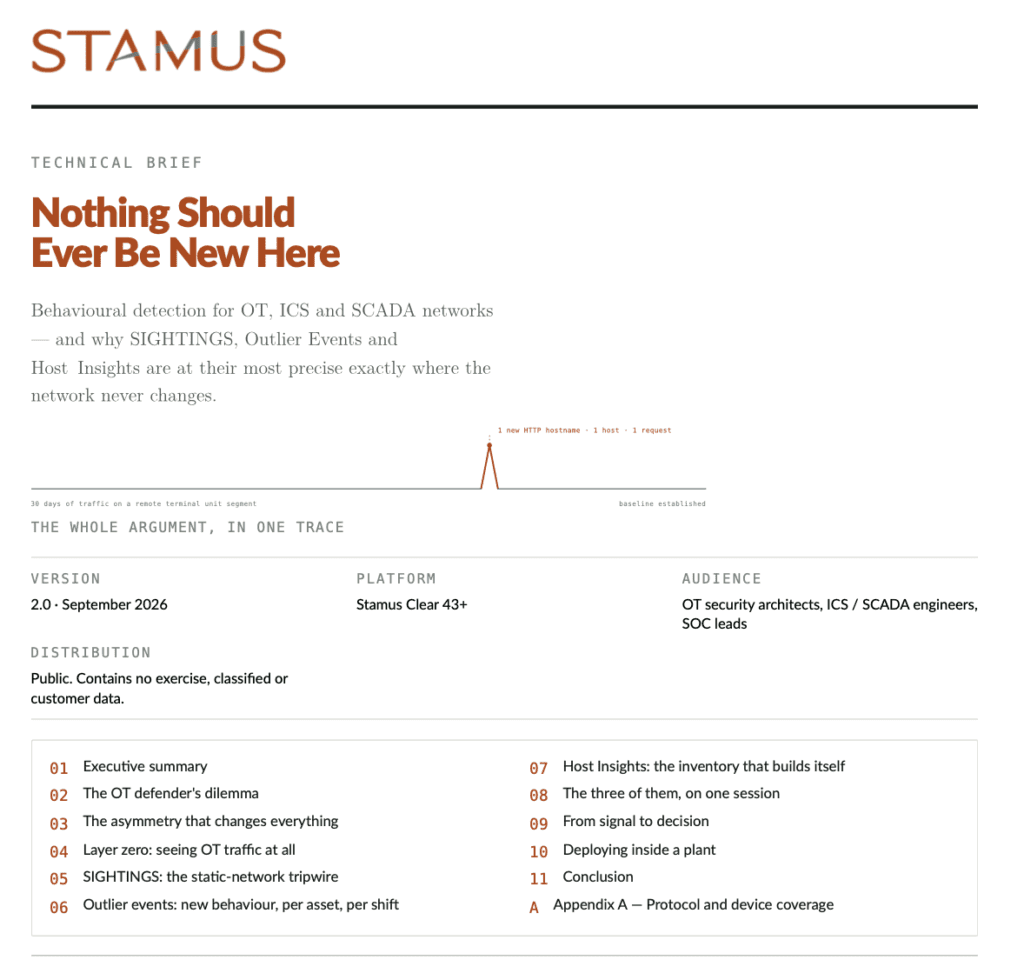
Download the Stamus OT Security Technical Brief
Why change detection fails in IT and works in OT
Novelty detection has a poor reputation in corporate IT, where constant domain lookups, browser updates, and changing file shares create relentless noise. In a control cell, however, communication patterns stabilize within days. According to Stamus, after roughly a week of learning, the count of genuinely new network artifacts on an OT segment falls to approximately zero.
Against that flat baseline, a new hostname or unfamiliar SSH client stands out instantly. In OT, change control, maintenance windows, and clear cell ownership make every anomaly immediately actionable: the question isn’t whether a new event is malicious, but who authorized it.
Three ways to see change, without touching a controller
This is not an IT tool in an OT costume. Stamus Clear passively decodes industrial protocols down to the transaction level, allowing hunts based on Modbus function codes, DNP3 objects, or MQTT topics rather than simple IP addresses and ports:
IEC 60870-5-104 · Modbus · DNP3 · EtherNet/IP (CIP) · Siemens S7 · BACnet · OPC · MQTT
By analyzing a mirror copy of network traffic from a TAP or SPAN port, Stamus Clear delivers three primary change-detection capabilities:
- SIGHTINGS record all first-ever-seen IP/MAC addresses, DNS names, TLS/JA4 fingerprints, and filenames across the enterprise;
- Outlier Events flag anomalous behaviour tailored to operational shifts (e.g., distinguishing a 10:00 AM program download from an unexpected 3:00 AM modification); and
- Host Insights maintains a passive, self-updating asset inventory tracking over 60 attributes per device.
The full technical brief details how these mechanisms map against each phase of an intrusion before an attacker ever touches an industrial protocol.
Why this matters in Canada now
Canadian industrial networks face active targeting. In late 2025, The Canadian Centre for Cyber Security warned of unauthorized tampering with internet-exposed water facility pressure valves, oil and gas tank gauges, and agricultural silos. These incidents relied on valid commands from unauthorized sources—precisely the activity signature matching misses and change detection catches.
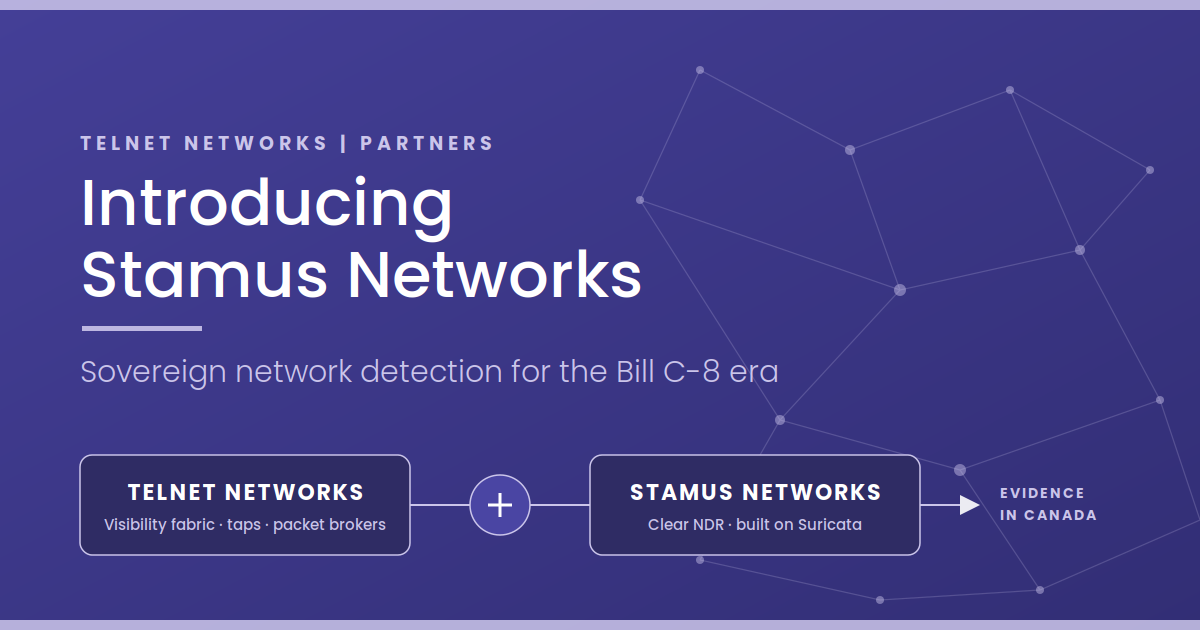
Concurrently, regulatory expectations are shifting from basic controls to verifiable proof. As Bill C-8 (the Critical Cyber Systems Protection Act) comes into force, it will require designated operators of critical infrastructure to actively detect and report cyber incidents. We have covered what the Act means for operators and for the vendors who serve them. C-8 is new to Canada, but the problem isn’t. Europe’s NIS2 Directive has asked operators for much the same since 2024, and Stamus’ platform offers a battle-tested approach already proven against comparable European regulatory frameworks.
Why Stamus
Built on Suricata, the open-source detection engine, Stamus Clear delivers, passive network visibility into PLCs, HMIs, and legacy devices where agents cannot run. Findings are delivered as actionable Declarations of Compromise with full transaction logs and packet captures attached, allowing analysts to explain alerts clearly to plant managers. With full support for on-premise, air-gapped execution, and seamless SIEM/SOAR export, operational data remains strictly within operator control.
Get the brief
The full 8-page technical brief provides a deeper breakdown of probe placement, network zone definitions, air-gapped deployment strategies, and stage-by-stage intrusion mapping.
Download the Stamus OT Security Technical Brief
Telnet is Stamus’s partner in Canada. You can read more about Stamus Clear on our partner page and in our post introducing the partnership. To discuss passive monitoring architecture for your plant or utility, contact the Telnet team.