Skip to content
Customers frequently seek information and recommendations from Safran about hardening security, including general guidelines about available network security features, jamming and spoofing deterrence, bug fixes, and networking-related issues.

Sometimes they’re in search of specific practices for time servers and clients. Sometimes, because SecureSync®/9483 is part of critical infrastructure, they may not fully understand all the issues related to timing, such as GNSS jamming/spoofing, NTP vulnerability or the various types of network attacks.

Generally speaking, the correct answers are specific to each networking infrastructure and each customer’s policies. However, there are some general guidelines to follow to harden security on your SecureSync®/9483, and this document should help. It covers the following areas and explains how to use each to prevent cyberattacks:

  • Authentication and authorization
  • HTTPS and SSL
  • SSH
  • SCP
  • SFTP with public/private support

This document also consolidate the recommendations from various product manuals into one handy location. They identify each security feature, shows default settings and offers recommendations about whether you should choose to enable it.

To make it easier, we’ve also provided links to the online manuals for each protocol — so configuration help is just a click away.

Supporting Material

TECH TIP: SECURESYNC 1200 SECURITY HARDENING RECOMMENDATIONS
Related Posts

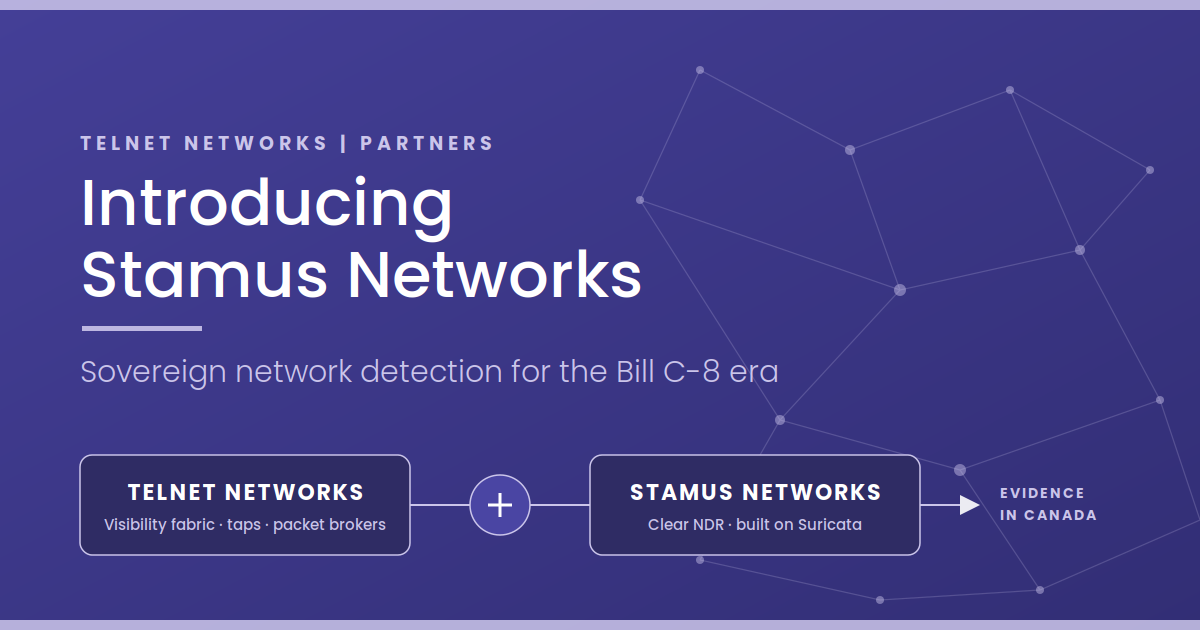
Introducing Stamus Networks: Network Security Built For The Bill C-8 Era

Introducing Stamus Networks: Network Security Built For The Bill C-8 Era

The ground shifted in June Bill C-8 received Royal Assent in June. For designated operators in telecommunications, energy, finance, nuclear…
From Vienna to CERN: The European Innovation Behind Modern Network and Timing Infrastructure

From Vienna to CERN: The European Innovation Behind Modern Network and Timing Infrastructure

Sub-nanosecond timing over Ethernet was not born in a product roadmap. It came out of CERN, where physicists needed the…
Encrypted Client Hello Is Here. What Can Your Network Tools Still See?

Encrypted Client Hello Is Here. What Can Your Network Tools Still See?

In March 2026 the IETF published RFC 9849, standardizing TLS Encrypted Client Hello. In plain terms, the part of the…
Vendor Spotlight: Simplifying Facility Synchronization with Novanex Solutions

Vendor Spotlight: Simplifying Facility Synchronization with Novanex Solutions

When timing is everything, clear visibility and precise data are non-negotiable. They form the backbone of your facility’s safety, compliance,…
Your AI Cluster Doesn't Need Sub-Nanosecond Timing. Your Campus Does.

Your AI Cluster Doesn't Need Sub-Nanosecond Timing. Your Campus Does.

Timing architecture for the AI campus, and where White Rabbit actually belongs. Every timing vendor now has an AI page.…