Skip to content

In this Webinar John Olson, from NetFlow Auditor, discusses the top 10 Best Practices for using Netflow data to analyse, report and alert on multiple aspects of Network traffic.

These best practices include:

  • Understanding where is the best place in your network to collect netflow data from
  • How long you should retain your flow data
  • Why you should archive more than just the top 100 flows
  • When static thresholds should be replaced by adaptive thresholds
  • More…

b2ap3_thumbnail_Fotolia_33050826_XS_20151006-142344_1.jpg

Thanks to NetFlow Auditor for the article.  
Related Posts

Upcoming Webinar: Show Me the Record: Turning Cyber Controls into Bill C-8 Evidence

Upcoming Webinar: Show Me the Record: Turning Cyber Controls into Bill C-8 Evidence

Bill C-8 (which enacts the Critical Cyber Systems Protection Act) became law in June 2026, shifting Canadian critical infrastructure from…
SecureSync PHP2Shell vulnerability: what to do now

SecureSync PHP2Shell vulnerability: what to do now

Safran has confirmed that the SecureSync PHP2Shell vulnerability affects the SecureSync 1200 and 2400, VersaSync, NetClock 9400 series and White…
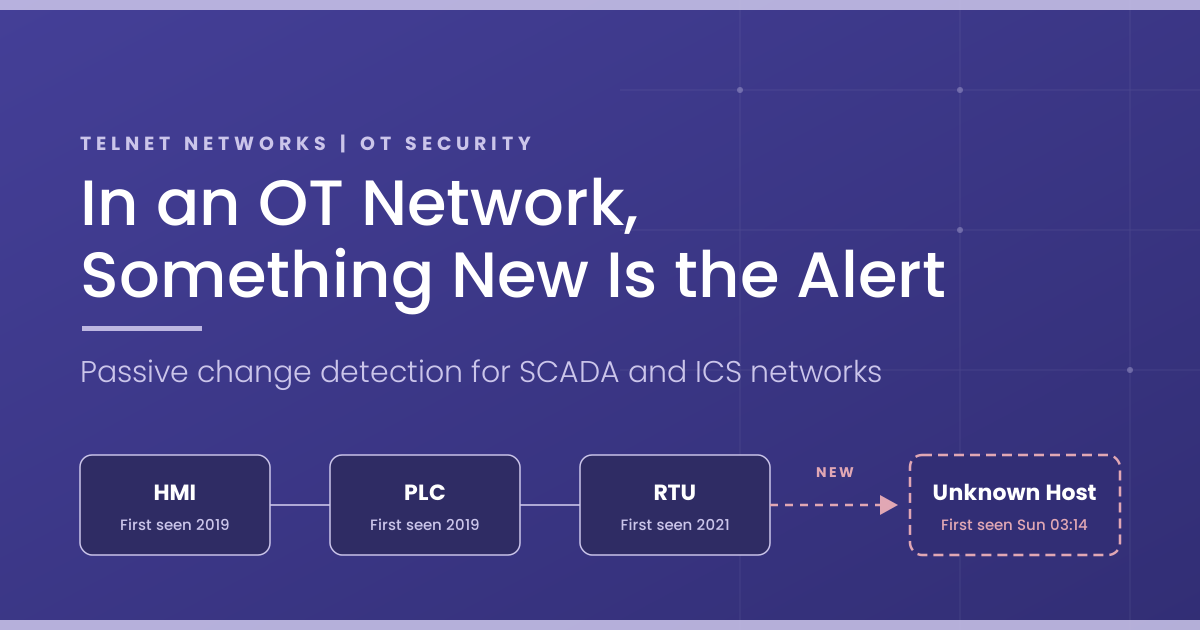
In an OT Network, Something New Is the Alert

In an OT Network, Something New Is the Alert

OT network change detection sounds like a compliance checkbox. In practice, it is one of the most precise detection methods…
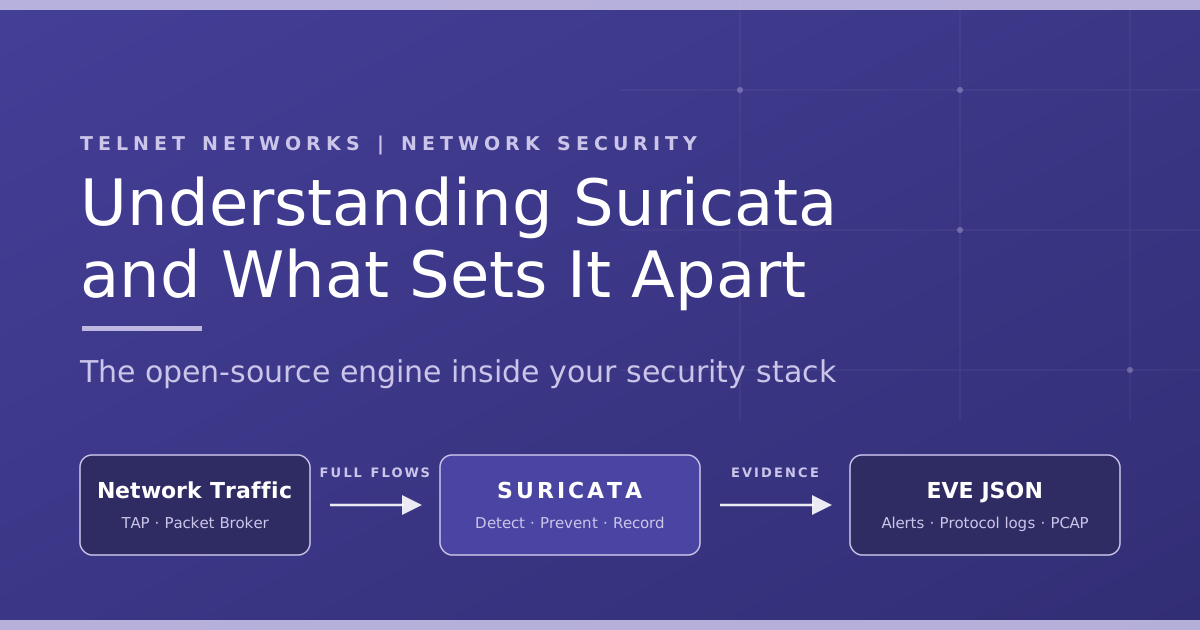
Understanding Suricata: The Open-Source Engine Inside Your Security Stack

Understanding Suricata: The Open-Source Engine Inside Your Security Stack

There is a good chance Suricata already runs somewhere in your network, even if nobody on your team has ever…
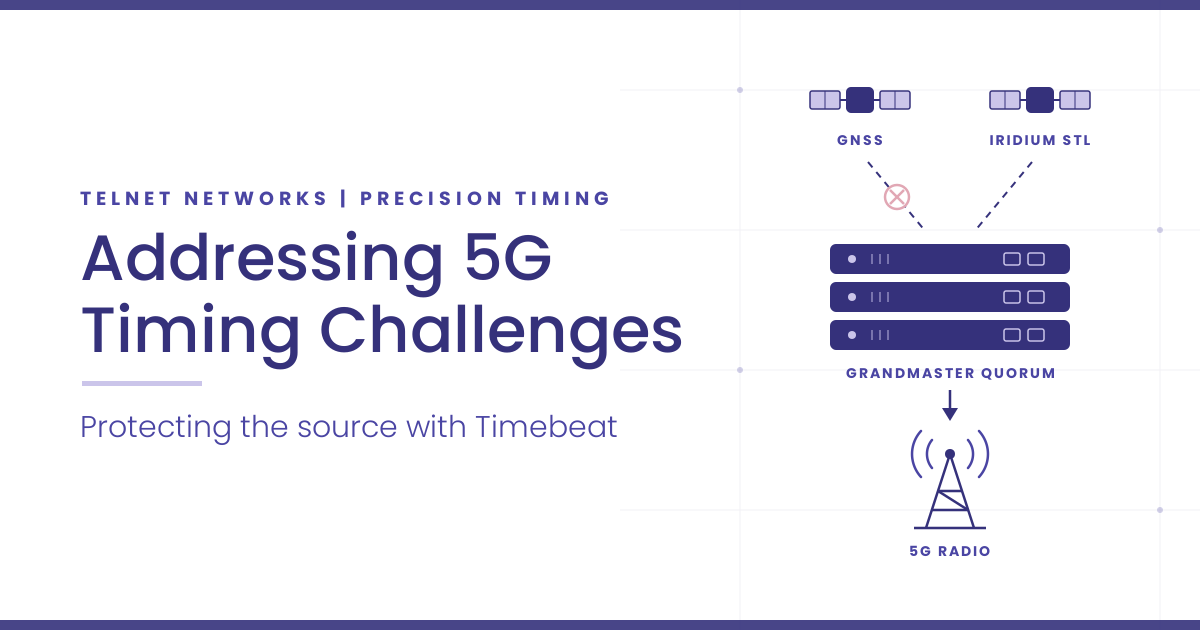
Addressing 5G Timing Challenges with Timebeat: What Canadian Carriers Can Fix at the Source

Addressing 5G Timing Challenges with Timebeat: What Canadian Carriers Can Fix at the Source

Most 5G timing challenges trace back to one rule. Canada’s mid-band 5G, in the 3500 MHz and 3800 MHz bands,…