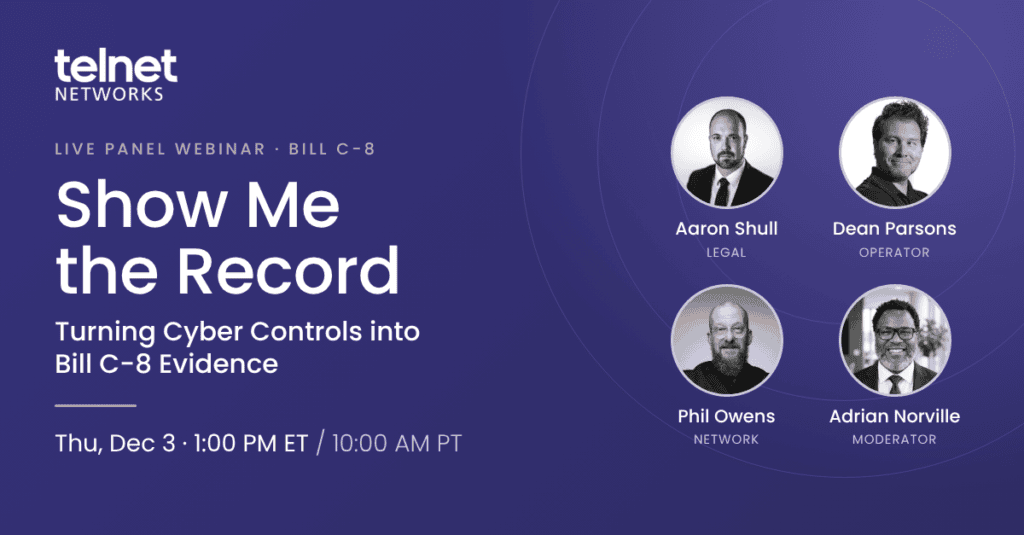
Upcoming Webinar: Show Me the Record: Turning Cyber Controls into Bill C-8 Evidence

C-8 Webinar poster

Bill C-8 (which enacts the Critical Cyber Systems Protection Act) became law in June 2026, shifting Canadian critical infrastructure from voluntary security guidelines to strict, enforceable mandates. Under the new rules, designated operators will have just 90 days to establish a documented cybersecurity program and will face a strict 72-hour window to report incidents. For tech and security teams, having cyber controls in place is no longer enough—you now have to actively prove they work.

The Act names six federally regulated services and systems deemed vital to national security or public safety. They include: telecommunications services, interprovincial or international pipelines and power lines, nuclear energy, transportation within federal authority, banking, and clearing and settlement.

Whether you are directly managing critical infrastructure or you’re a tech supplier who will soon see C-8 compliance requirements appearing in customer contracts, understanding how to produce defensible network evidence is now essential.

To help teams navigate these new regulatory expectations, Telnet Networks is hosting a live panel discussion: Show Me the Record: Turning Cyber Controls into Bill C-8 Evidence.

Webinar Details:

  • Date: Thursday, December 3, 2026
  • Time: 1:00 PM ET (10:00 AM PT)
  • Format: 60-minute live panel discussion with audience Q&A (replay available for registrants)

This session is a real discussion, not a series of presentations. Moderated by Telnet Networks President Adrian Norville, the panel brings legal, operator, and network views to the same questions, and they will not always agree. You will hear from our expert panel as they break down what the Act requires and what is still unknown. They will also cover what operators can realistically show in complex OT environments and how to turn network traffic into a record you can present to your board, the Cyber Centre, and your regulator.

About The Panelists

Aaron Shull (Shull Law)

Aaron Shull is principal of Shull Law and a senior fellow at the Centre for International Governance Innovation (CIGI), where he was previously managing director and general counsel. He advises business and government on cybersecurity, incident response, privacy and AI governance, and has testified before House of Commons and Senate committees.

Dean Parsons (ICS Defense Force, SANS)

Dean Parsons is CEO of ICS Defense Force and a SANS Principal Instructor, with more than 20 years in industrial control systems (ICS) and operational technology (OT) cybersecurity. He advises boards, executives and operations teams on cyber resilience, incident response and defensible architectures across critical infrastructure.

Phil Owens (Stamus Networks, SANS) 

Phil Owens is Vice President, Customer Solutions at Stamus Networks, where he leads systems engineering, support and customer success. He has more than 20 years of experience in IT, networking and cybersecurity as a systems engineer and product manager, with earlier roles at RSA Security, AT&T and IBM, and he served in the United States Air Force.


Whether you lead security at an organization likely to be designated under the Act, manage infrastructure teams tasked with producing network evidence, or handle contracts where C-8 compliance terms will soon appear, this session will give you a practical path forward. Registration takes under a minute, and even if you cannot join live on December 3, everyone who signs up will receive the full recording and session materials afterward. 

Register for the webinar here.
Introducing Stamus Networks: Network Security Built For The Bill C-8 Era

Telnet Networks and Stamus Networks partnership lockup over a network topology motif, announcing Stamus Networks Canada partnership

The ground shifted in June

Bill C-8 received Royal Assent in June. For designated operators in telecommunications, energy, finance, nuclear and transportation, the Critical Cyber Systems Protection Act (CCSPA) brings a 90-day clock to stand up a cyber security program once a class of operators is designated, an incident-reporting window capped at 72 hours, and a continuing duty to identify and mitigate supply-chain risk. That last obligation does not stop at the operator’s front door. It flows down to the vendors and integrators who serve them. The telecom provisions are already in force; the CCSPA itself is law and awaits its in-force order.

None of this arrives in a vacuum. Ransomware crews and state-sponsored actors have been attacking Canadian utilities, transit systems and government networks for years. At the same time, the question of where security telemetry lives, and who can compel access to it, has moved from a procurement footnote to a board-level concern. Data sovereignty is now a security requirement, not a preference.

That is the context in which we went looking for a network security partner. We were not looking for just the loudest platform on the floor. We wanted one that turns network activity into answers teams can act on, backs each finding with evidence and disclosed detection logic, and runs in the environments our customers actually operate.

We chose Stamus Networks and its Stamus Clear network security platform.

Meet Stamus Clear

Stamus Networks is the creator of Stamus Clear, a network security platform built on Suricata, the open-source network security engine much of the industry runs on. Stamus Clear turns network traffic into clear, evidence-backed answers about what is happening on the network, so teams can see what the rest of the stack misses and know what to do about it.

Stamus Clear watches the network itself. Endpoints get missed, logs get altered, and nobody is installing an agent on a substation controller or a signalling system. But every attacker has to cross the wire at some point, which makes the network the one layer they cannot avoid touching. Stamus Clear turns that traffic into a short,  list of response-ready cases: what happened, what to do next, and the evidence and reasoning behind it. Clear Detect raises high-confidence Declarations of Compromise and Declarations of Policy Violation rather than handing the team another queue of alerts or a score it has to trust.

That evidence is the point. When an incident happens, the questions come fast. What did the attacker touch? When did it start? What left the building? Can you prove it? A team running Stamus Clear can answer with evidence it can inspect and defend, and show its work to whoever is asking, whether that is the board, an auditor or a regulator.

Deployment is on your terms. Stamus Clear runs on-premise or in hybrid environments, including fully air-gapped deployments, with no dependency on a Stamus cloud. The customer keeps its network data under its own control.

A decade of proof

Stamus has been building on Suricata since 2014, founded by Eric Leblond and Peter Manev, two of the people behind the open-source engine. The team remains at the core of the Suricata project through the OISF. That depth matters: Stamus is not simply integrating the engine; it brings more than a decade of expertise turning network traffic into evidence teams can act on.

The customer list tells the rest of the story. Stamus is trusted by European national banks, EU institutions, government, critical infrastructure and global industrial operators: organizations that get attacked most and can least afford a finding they cannot explain. The team has also supported a decade of NATO cyber defender training. That track record, together with 97% net customer retention, is proof built over years rather than a marketing claim.

What settled it for us, though, was their approach. Stamus is transparent by design: for detections built on defined detection methods, analysts can inspect the detection logic that fired and the traffic evidence behind it; anomaly detections carry the evidence and reasoning behind the finding. Stamus Clear also integrates with the security tools customers already run. When you have to defend a decision to an auditor or a regulator, evidence and logic you can check are a very different proposition from a black-box score you are asked to trust.

From the fibre to the finding

For more than two decades, Telnet has designed and supplied the visibility fabric (network taps, packet brokers and aggregation) that Canadian utilities, telecoms, transit agencies, government departments and industry run. That fabric decides what a security tool can see. NDR is only as good as the traffic it is fed, and we have expertise in building the layer that feeds it.

Together, Telnet and Stamus deliver the complete evidence pipeline, from the fibre to the finding. We scope the traffic access, Stamus Clear turns network activity into prioritized, response-ready cases and evidence, and the whole chain stays in the customer’s custody.

We built this partnership for specific deployment realities: organizations that cannot send telemetry to a vendor cloud; air-gapped, OT and industrial networks where an agent will never be installed; and operators who will need audit-ready records as the CCSPA reporting obligations come into force. If you already run taps and brokers, Stamus Clear can be added to your existing visibility fabric, shortening the path from traffic access to useful, evidence-backed answers.

“Canadian critical infrastructure operators increasingly need control over where security data is processed and the ability to show exactly why a finding was made. Telnet Networks brings the local visibility expertise; Stamus Clear brings evidence-backed network security that can run on-premise or fully air-gapped. Together, we give operators a practical path from network traffic to answers they can act on without depending on a vendor cloud.”
— Mark Firmin, CEO, Stamus Networks

What happens next

Two things you can do today. Book a C-8 Readiness Briefing: 45 minutes with our team on what the Act requires, where the evidence gaps usually sit, and how to prepare for designation. Or ask us about a proof of concept on your existing visibility infrastructure.

Over the coming weeks we will go deeper on the questions this partnership was built to answer: what audit-ready network evidence actually looks like, why control of security data matters, how detection works in an air-gapped environment, and how to get ahead of the supply-chain questionnaires that C-8 will bring.

Welcome, Stamus Networks. We are glad to have you alongside us.