Bill C-8 (which enacts the Critical Cyber Systems Protection Act) became law in June 2026, shifting Canadian critical infrastructure from voluntary security guidelines to strict, enforceable mandates. Under the new rules, designated operators will have just 90 days to establish a documented cybersecurity program and will face a strict 72-hour window to report incidents. For tech and security teams, having cyber controls in place is no longer enough—you now have to actively prove they work.
The Act names six federally regulated services and systems deemed vital to national security or public safety. They include: telecommunications services, interprovincial or international pipelines and power lines, nuclear energy, transportation within federal authority, banking, and clearing and settlement.
Whether you are directly managing critical infrastructure or you’re a tech supplier who will soon see C-8 compliance requirements appearing in customer contracts, understanding how to produce defensible network evidence is now essential.
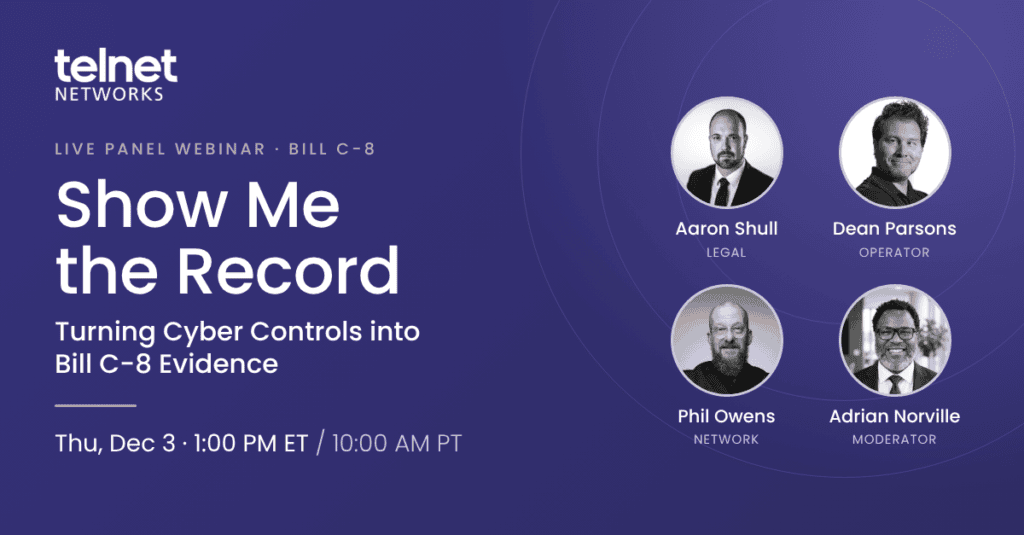
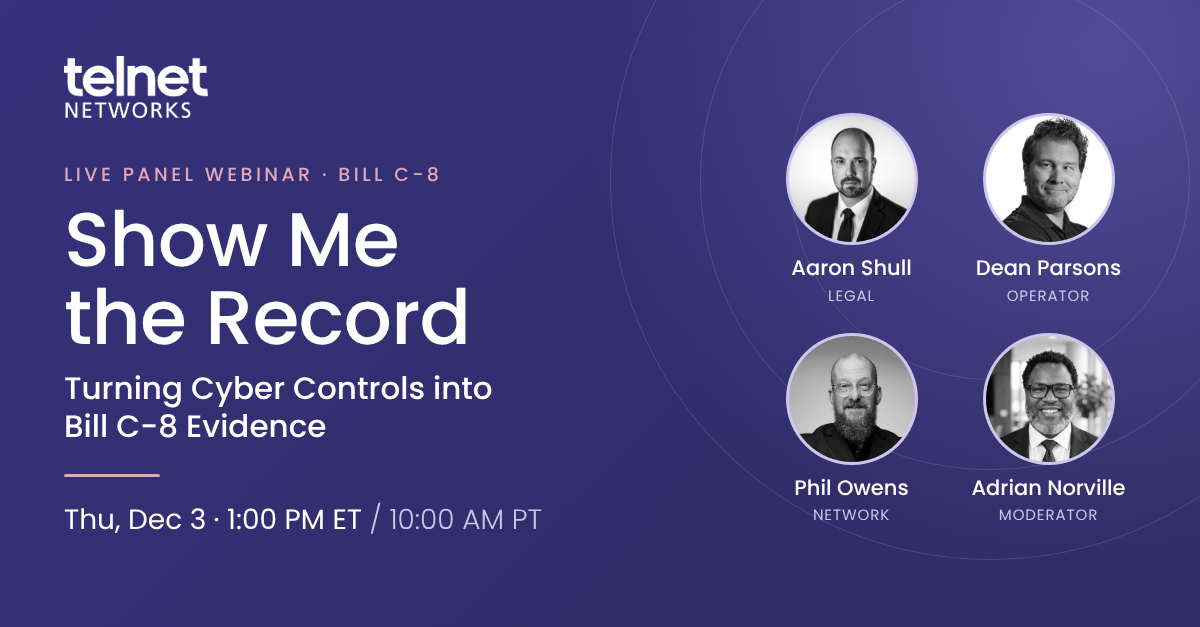
To help teams navigate these new regulatory expectations, Telnet Networks is hosting a live panel discussion: Show Me the Record: Turning Cyber Controls into Bill C-8 Evidence.
Webinar Details:
- Date: Thursday, December 3, 2026
- Time: 1:00 PM ET (10:00 AM PT)
- Format: 60-minute live panel discussion with audience Q&A (replay available for registrants)
This session is a real discussion, not a series of presentations. Moderated by Telnet Networks President Adrian Norville, the panel brings legal, operator, and network views to the same questions, and they will not always agree. You will hear from our expert panel as they break down what the Act requires and what is still unknown. They will also cover what operators can realistically show in complex OT environments and how to turn network traffic into a record you can present to your board, the Cyber Centre, and your regulator.
About The Panelists
Aaron Shull (Shull Law)
Aaron Shull is principal of Shull Law and a senior fellow at the Centre for International Governance Innovation (CIGI), where he was previously managing director and general counsel. He advises business and government on cybersecurity, incident response, privacy and AI governance, and has testified before House of Commons and Senate committees.
Dean Parsons (ICS Defense Force, SANS)
Dean Parsons is CEO of ICS Defense Force and a SANS Principal Instructor, with more than 20 years in industrial control systems (ICS) and operational technology (OT) cybersecurity. He advises boards, executives and operations teams on cyber resilience, incident response and defensible architectures across critical infrastructure.
Phil Owens (Stamus Networks, SANS)
Phil Owens is Vice President, Customer Solutions at Stamus Networks, where he leads systems engineering, support and customer success. He has more than 20 years of experience in IT, networking and cybersecurity as a systems engineer and product manager, with earlier roles at RSA Security, AT&T and IBM, and he served in the United States Air Force.
Whether you lead security at an organization likely to be designated under the Act, manage infrastructure teams tasked with producing network evidence, or handle contracts where C-8 compliance terms will soon appear, this session will give you a practical path forward. Registration takes under a minute, and even if you cannot join live on December 3, everyone who signs up will receive the full recording and session materials afterward.
Register for the webinar here.