From Vienna to CERN: The European Innovation Behind Modern Network and Timing Infrastructure

Sub-nanosecond timing over Ethernet was not born in a product roadmap. It came out of CERN, where physicists needed the White Rabbit protocol to synchronize instruments across a particle accelerator with a precision that ordinary networking had no reason to attempt. The specification is now folded into IEEE 1588-2019 as the High Accuracy profile, and it has quietly become the reference point that timing vendors across Europe still measure themselves against.

That is a useful way to think about a handful of the vendors in Telnet’s own portfolio. They are not the biggest names in their categories, but they tend to be the ones doing the interesting engineering: a packet broker maker in Vienna, a clockmaker in western France that has been keeping time since before the telephone, a Suricata-based security platform built by open-source developers in Paris. Here is what each of them has been building lately.

Cubro: Precision Engineering With New Backing

Cubro has been designing network packet brokers, TAPs and probes out of Vienna since 2003, and in December 2025 the Swedish industrial group Addtech acquired a majority stake in the company. For a Telnet customer, the practical upshot is stability: Cubro keeps its Vienna engineering team and roadmap, now with a publicly traded parent behind it (Addtech trades on Nasdaq Stockholm).

The product itself keeps moving. Cubro’s Omnia platform runs application-layer classification directly on the packet broker, an architecture the company has been pushing further as encrypted traffic makes payload-based inspection less useful across the industry. It is the same “classify once, distribute everywhere” idea that shows up increasingly in how Telnet evaluates network visibility architecture generally, and Cubro is one of the vendors building toward it in hardware.

Profitap: Forty Years of TAPs, Reshaped for OT

Profitap’s roots go back to 1984 in Strasbourg, France, before the company relocated its headquarters and R&D to Eindhoven, Netherlands. That history matters less than what the team has done recently with it: the IOTA platform extends Profitap’s TAP and packet-broker lineage into portable, high-precision capture kits built for operational technology networks, where nanosecond-level timestamp accuracy in packet capture is often the difference between a diagnosable incident and a guess.

Profitap’s engineering has always leaned toward the physically compact and the field-deployable, and IOTA is the clearest expression of that instinct: fly-away capture kits that a field engineer can carry to a substation or a plant floor rather than a rack that has to be provisioned in advance.

Infosim: A University Spin-out That Stayed Independent

Infosim was founded in 2003 as a spin-out from the University of Würzburg, and more than twenty years later it is still headquartered there, still privately held, and still developing StableNet entirely out of its German R&D team. That kind of continuity is unusual in network management software, where consolidation is the norm.

StableNet’s release cadence has stayed active through that independence. Its unified approach to fault, performance and configuration management remains vendor-agnostic by design, which is a deliberate choice for a company that could have built a walled garden and didn’t.

Timebeat: Timing Software Built on Open Standards

Timebeat is a UK company building PTP and NTP synchronization as software first, hardware second, which is close to the opposite of how most of the timing industry has historically worked. Its stated position on vendor lock-in is blunt: interoperability is the point, not a concession. The Timebeat.app daemon replaces chrony, ntpd and ptp4l on a host, and the company’s grandmaster hardware line extends the same open approach into rack appliances and PCIe timecards.

Timebeat also builds explicitly for interoperability with White Rabbit-based networks, which is the same protocol lineage that opened this post. It is a small detail, but it says something about how connected European timing engineering still is to that original CERN work, even decades and several product categories removed from it.

Bodet: From Mechanical Clockmaking to Network Time

Bodet has been making clocks in Trémentines, France since the 19th century, long enough that the company’s own history predates the electrical grid it now helps synchronize. The relevant point for a network engineer is less the heritage and more what Bodet has done with it: its Netsilon line brings that clockmaking precision into NTP and PTP master clock appliances built for the same digital infrastructure everyone else in this post is building for.

Telnet has deployed Bodet clock systems where functional requirements could not be met by any other vendor and operational requirements were absolute. Performance has always met or exceeded the required standards.

Stamus Networks: Open-source Security Engineering Out of Paris

Stamus Networks was founded in 2014 by Éric Leblond and Peter Manev, both long-time core developers of Suricata, the open-source intrusion detection engine that much of the network security industry builds on in one form or another. Stamus is dual-headquartered in Paris and Indianapolis, but its product engineering and much of its leadership remain rooted in the same open-source security community that produced Suricata in the first place.

Clear NDR, Stamus’s flagship platform, turns that Suricata foundation into a full network detection and response system, and the company has kept contributing back to the open-source project rather than treating it purely as a dependency. That is a meaningfully different posture from most commercial NDR vendors, and it shows in how transparent Clear NDR is about what it is actually doing under the hood.

The Common Thread

None of these companies are chasing the same trend at the same time. Cubro is scaling with new capital behind it. Profitap is pointing forty years of TAP engineering at OT networks. Infosim has stayed independent long enough to keep StableNet vendor-agnostic on principle. Timebeat is building timing software that assumes interoperability rather than lock-in. Bodet is doing to network time what it has done to mechanical clocks for over a century. Stamus is building commercial security on an open-source foundation it still maintains.

What connects them is a certain patience with hard engineering problems, the same patience that turned a CERN physics requirement into an IEEE standard. Telnet works with all six because each one solves a specific, technical problem well, not because of where they happen to be headquartered. But it is worth noticing, occasionally, how much of the interesting work in this industry keeps coming out of the same part of the world.

Want to know where any of these fit into your network? Get in touch with our team and we’ll help you figure out what makes sense.

Introducing Cubro’s EXA48800: Advanced Network Visibility for High-Speed Infrastructure

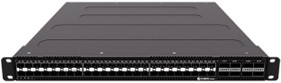
EXA48800 Network Packet Broker

In today’s complex digital environments, where data moves at extreme speeds and network architectures span multiple layers, visibility is no longer optional. The Cubro EXA48800 Network Packet Broker is a high-performance visibility appliance designed to give network, security, and operations teams the clarity they need to monitor, analyze, and secure even the most demanding infrastructures.

EXA48800: Power and Precision for Modern Network Visibility

EXA48800 Network Packet Broker image

The EXA48800 stands at the forefront of Cubro’s network visibility portfolio, purpose-built for high-speed environments where performance, accuracy, and flexibility are non-negotiable. Designed to handle everything from 10 Gbps access links to 100 Gbps backbone traffic, it combines a multi-core programmable switch with dual high-performance ARM CPUs to deliver exceptional processing power and control.

Built to Handle Today’s Most Demanding Networks

Intelligent multi-speed traffic filtering and balancing – Seamlessly supports 1, 10, 25, 40, and 100 Gbps links, ensuring the right traffic reaches the right monitoring and security tools without overload.

High-density, flexible port design – Up to 48 ports for 10/25 Gbps and 8 ports for 40/100 Gbps provide the scalability and breakout flexibility needed to adapt as networks evolve.

Advanced packet inspection – Full IPv6 support and deep packet payload filtering deliver richer insight into modern traffic patterns beyond basic headers.

Comprehensive tunnel awareness – Unlock visibility into encapsulated traffic by filtering inside VXLAN, MPLS, GTP, ERSPAN, and other tunnels, eliminating blind spots across overlay networks.

More than a packet broker, the EXA48800 is a powerful traffic intelligence platform that delivers precisely curated data to each connected tool, maximizing value while minimizing noise.

Why the EXA48800 Makes a Difference

Expose hidden traffic – As networks grow more virtualized and encrypted, critical data often disappears into tunnels. The EXA48800 brings that traffic back into view, helping teams quickly identify performance issues and security threats.

Get more from your tools – By filtering, deduplicating, and optimizing traffic before it reaches monitoring and security platforms, the EXA48800 improves tool efficiency, reduces processing strain, and accelerates time to insight.

Invest with confidence – Built with a future-ready architecture that supports higher speeds, modern protocols, and flexible port configurations, the EXA48800 is designed to scale with your network and protect your investment over time.

Ideal for Complex, High Velocity Networks

The EXA48800’s advanced features make it an ideal solution for organizations operating large, complex, and high-velocity networks:

  • Cloud and Service Providers (Telcos): The deep tunnel awareness (VXLAN, MPLS, GTP) is essential for monitoring complex, virtualized backbone traffic and ensuring service quality across their vast, multi-layer architectures.
  • Large Enterprises and Data Centers: Any organization with a high-speed backbone (40/100 Gbps) and high-density port requirements will find the EXA48800 critical for reducing processing strain on their security and monitoring platforms.
  • Network Operations (NetOps) and Security Operations (SecOps) Teams: By filtering, deduplicating, and optimizing traffic, the EXA48800 ensures each monitoring or security tool receives only the precise data it needs. This improves tool efficiency and accelerates time to insight, enabling faster identification of critical performance issues and security threats.

The Advantage of Transparent Licensing

Beyond technical performance, the EXA48800, and Cubro’s entire Packet Broker lineup offers a significant operational and financial advantage when compared to vendors like Gigamon and Keysight: a simple licensing model.

  • No Additional Fees for Essential Features: Cubro believes essential intelligence should be built-in. This means the powerful core capabilities, including comprehensive tunnel awareness (VXLAN, MPLS, GTP, ERSPAN) and advanced packet inspection, are available without the need for expensive add-on licenses.
  • Invest with Confidence: Cubro’s architecture is designed to scale with your network and protect your investment over time. This approach eliminates the “surprise cost” of future feature activation or annual fees to keep your hardware from turning into a paperweight.

This streamlined approach reduces unnecessary operational complexity and ensures you get the maximum value from your network visibility platform from day one.

As networks scale and traffic patterns grow more dynamic, the need for intelligent visibility becomes critical. The Cubro EXA48800 meets this challenge with high throughput, flexible filtering, tunnel awareness, and powerful traffic engineering, making it a strong foundation for organizations that rely on real time performance, security insights, and efficient tool utilization.

If this product is something you would like to discuss for your infrastructure, please contact our sales team today.

Bypass Switches: Ensuring Network Uptime and Security in High-Stakes Environments

Modern Bypass Switches also offer granular control and flexible configurations, allowing administrators to choose whether the device should fail open to prioritize uptime or fail closed to prioritize security. With features like remote management, logging, alerting, and the ability to validate inline devices during maintenance, they provide both visibility and control. This makes them particularly valuable in high-volume, low-latency, or encrypted traffic environments, allowing organizations to maintain security and operational continuity without compromise.

Vendors like Keysight, Cubro, Profitap, and Garland offer Bypass Switches and visibility solutions that prevent inline security tools from becoming single points of failure. By monitoring device health with heartbeat packets, link-state checks, and latency thresholds, these switches can automatically reroute traffic to maintain uninterrupted network operations in the event of an appliance failure or congestion.

What is a Bypass Switch

A Bypass Switch is a fail-safe device that maintains continuous traffic flow when an inline security appliance such as an IPS or firewall becomes unavailable. Under normal conditions, the switch directs all packets through the security device for inspection, filtering, and threat prevention. If the appliance fails, loses power, or must be taken offline for maintenance, the Bypass Switch instantly reroutes traffic around it to prevent downtime and keep the network operational.

To achieve this, the switch continuously monitors the health of the inline device using heartbeat packets, power detection, and link-state checks. As long as the heartbeats return, the appliance stays in the path. If the heartbeats are interrupted or performance thresholds are exceeded, the switch enters bypass mode and allows traffic to pass directly between network ports. This approach preserves uptime and enables organizations to service or replace security equipment without disrupting live traffic.

How External Bypass Switch Failover Works Today

Modern Bypass Switches are designed to actively safeguard both performance and security rather than simply acting as a passive relay. They constantly measure link conditions and appliance responsiveness in real time, using mechanisms such as power detection, link-state analysis, heartbeat packets, and latency thresholds. When these metrics indicate an emerging problem, the switch automatically removes the inline device from the data path before end users experience disruption.

Advanced Bypass Switches offer granular policies and flexible configurations, allowing administrators to choose fail-open for uptime or fail-closed for security based on application needs. With built-in remote management, logging, and alerting, teams can see when and why failovers occur and even validate inline devices during maintenance. These capabilities make them especially valuable in environments with heavy encrypted traffic, low-latency transactions, or critical infrastructure, ensuring uninterrupted flow while preserving the required level of protection and visibility.

The Added Value of a Bypass Switch

Protects uptime: Automatically reroutes traffic if an inline security or monitoring tool fails, loses power, or requires maintenance.

Eliminates single points of failure: Prevents downtime and costly outages in high-availability or mission-critical environments.

Enables seamless maintenance: Lets you patch, upgrade, or replace IPS, IDS, firewalls, and other inline tools without interrupting live traffic.

Provides proactive monitoring: Uses heartbeat packets, link-state checks, and latency thresholds to detect performance issues early.

Maximizes security investments: Ensures your inline devices deliver their full value while minimizing operational and business risk.

Bypass Switches deliver the greatest value in environments where inline security tools such as IPS, IDS, firewalls, or DLP appliances are potential single points of failure. In high-availability networks, even brief outages caused by maintenance, software updates, or device crashes can disrupt business-critical applications. A Bypass Switch eliminates that risk by instantly routing traffic around the inline device if it becomes unresponsive or needs to be taken offline. This allows security teams to perform updates or swap hardware without interrupting live traffic.

They also shine in high-throughput or latency-sensitive applications, such as data centers, financial trading platforms, healthcare systems, and critical infrastructure, where uptime and reliability are paramount. By continuously monitoring link health with heartbeat packets and latency thresholds, bypass switches detect performance issues before they impact users. In these situations, they act as a safeguard that protects service continuity and ensures organizations get full value from their inline security investments without introducing new risks.

Contact our sales team today for a free consultation and quote on bypass switches tailored to your network needs.

Network Packet Brokers at the Inflection Point

The global network packet broker market hit USD $910 Million in 2024 and, according to Cognitive Market Research, is expected to grow at more than 7% annually through 2032. This growth is driven by the increasing demand for network visibility solutions that enhance security and performance across complex network infrastructures.

To support that growing demand and growth, key players like Cubro, Keysight Technologies, and Garland Technology introduced innovative solutions to enhance network visibility, security, and performance throughout 2024.

Cubro’s Level Up on Security

In 2024, Cubro Network Visibility received the ISO 27001:2022 certification, an acknowledgment of Cubro’s robust information security management systems and dedication to protecting customers from threats and ensuring that Cubro continues to lead in innovation and best practices in the industry. This certification followed the introduction of a next-generation network packet broker utilizing the latest P4 programmable processors in late 2023.

Garland Technology’s TradeUp Program

Garland Technology has introduced the TAP-IT & TradeUp Exchange program, allowing organizations to trade in outdated network TAPs and packet brokers for advanced solutions. This initiative ensures complete packet visibility by delivering a full platform of network TAPs, inline bypass, and packet broker products. Garland’s purpose-built NPBs include features such as aggregation, filtering, load balancing, deduplication, time stamping, and packet slicing, providing flexible and scalable solutions for future on-demand growth with excellent ROI.

Keysight Technologies’ Enhancements

In 2024, Keysight Technologies introduced the Vision Edge 400P (E400P), a next-generation network packet broker (NPB). Scalable from 10G to 400G The Vision 400 Series Network Packet Brokers received the prestigious 2024 Global New Product Innovation Award from Frost & Sullivan and achieves the highest port density for 400G in a 1RU form factor.

The developments in 2024 by Cubro, Keysight Technologies, and Garland Technology highlight the dynamic nature of the network packet broker market. As organizations continue to prioritize network visibility and security, these innovations play a crucial role in meeting the evolving challenges of modern network environments.

2025 Packet Broker Outlook

The global Network Packet Broker industry is on a trajectory of significant growth and innovation in 2025 driven by the increasing complexity of network infrastructures and the escalating demand for enhanced network visibility and security.

In 2025, leading Packet Broker OEMs are expected to focus on transformational features and developments in the following areas:

  • Integration Between On-Premise And Cloud Environments – The proliferation of cloud-based applications necessitates advanced NPB solutions to manage and monitor data traffic effectively, ensuring seamless integration between on-premise and cloud
  • Efficient Data Management And Network Optimization – The surge in internet multimedia content and web applications is contributing to higher data volumes, prompting organizations to invest in efficient data management and network optimization solutions
  • Integration of AI and Machine Learning – Deploying AI/ML to enhance real-time data analysis, automate network management tasks, and improve threat detection capabilities

Organizations are projected to continue investing heavily in advanced NPB solutions. These investments are expected to focus on enhancing network performance, security, and visibility and aligning with the dynamic landscape of digital transformation.